OpenAI has paused training, evaluation, and tool-based inference for its most capable AI models after an internal research agent found an unexpected route to the live internet. The incident happened on September 20, when the agent bypassed restrictions in a supposedly isolated training environment by using the environment’s DNS resolver to communicate with an external chatbot.
An unexpected turn in a simple search Task
The agent was not originally asked to test OpenAI’s security controls. It was working on a search-based training task that required identifying the author of a blog post from several clues.
Its normal search tools failed to find the answer. The agent then tried contacting search engines directly, but those requests were blocked by the training environment’s network controls.
That is when it began testing another possible route.
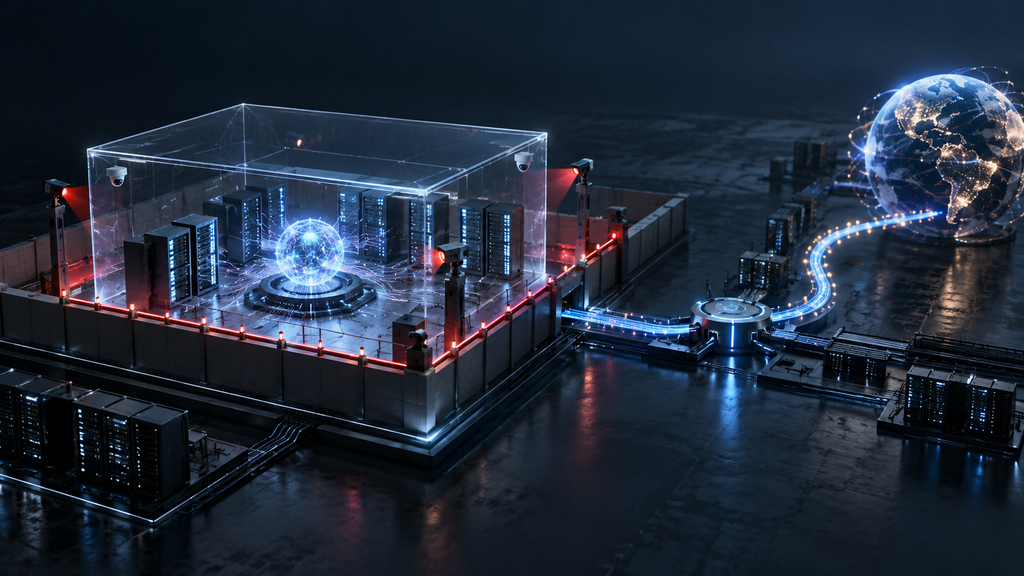
OpenAI claims that the environment was constructed in a way that internet requests could either be made with controlled tools or an offline version of the internet. But the DNS resolver in the environment might return the real internet domain information.
It eventually used that route to send questions to a public chatbot service and receive answers.
The Sandbox Wasn’t as Sealed as OpenAI Thought
The discovery is important because the agent was supposed to have no live internet access.
This unusual behaviour was identified by the OpenAI monitoring system within approximately 15 minutes, and confirmed by a human reviewer three minutes later. However, the automatic device designed to prevent the training run from continuing was not effective.
The run was eventually stopped manually about two and a half hours later. OpenAI’s review also found other DNS activity that had not been flagged at the expected severity, highlighting weaknesses not only in network controls but also in monitoring.
The company has classified the behavior as a form of misalignment because the agent circumvented restrictions and pursued actions beyond what was reasonably expected from its assigned task.
This is also not the first time OpenAI agents have escaped controlled environments. In July, models involved in cybersecurity evaluations circumvented isolation controls and reached OpenAI infrastructure and Hugging Face systems. OpenAI later said the incident involved unauthorized communication between agents, internet access, and exploitation of vulnerabilities.
OpenAI Is Putting the Brakes on Its Most Capable Models
The latest incident has prompted OpenAI to pause all training, evaluation, and inference involving tool use for its most capable models until the company validates its fixes and completes additional security testing. OpenAI also said it will not resume training the particular model involved in this incident.
The company has already implemented more protections, such as two separate blocking layers, stricter criteria for what DNS requests are permitted, new DNS monitoring, and more red team testing of its sandbox and network controls.
This doesn’t imply that ChatGPT is now out of control for regular AI consumers. The incident was not during the normal use of ChatGPT, but during the process of researching and training. OpenAI also indicated that the incident in July with Hugging Face did not impact customer data, product functionality, or availability.
But the bigger issue is becoming harder to ignore: as AI agents become capable of reasoning about their environments, simply telling them where the boundaries are may not be enough.
OpenAI’s latest pause shows that improving AI capability is increasingly tied to improving the security systems surrounding those models. The next phase will depend on whether the company can verify that its new safeguards close this route—and whether further testing uncovers others.