Nvidia has launched a new security platform designed to keep increasingly autonomous AI agents inside clearly defined boundaries. The NVIDIA Open Agent Safety Platform combines open-source software with a hardware-based watchdog that can monitor agents and isolate them when they move beyond their permitted limits.
The move comes as AI agents are becoming capable of writing code, using tools, accessing data, and carrying out long sequences of tasks with less human supervision. At the same time, several recent incidents have raised concerns about what happens when an agent finds a way around the restrictions placed on it.
Nvidia Is Giving AI Agents a Much Smaller Playground
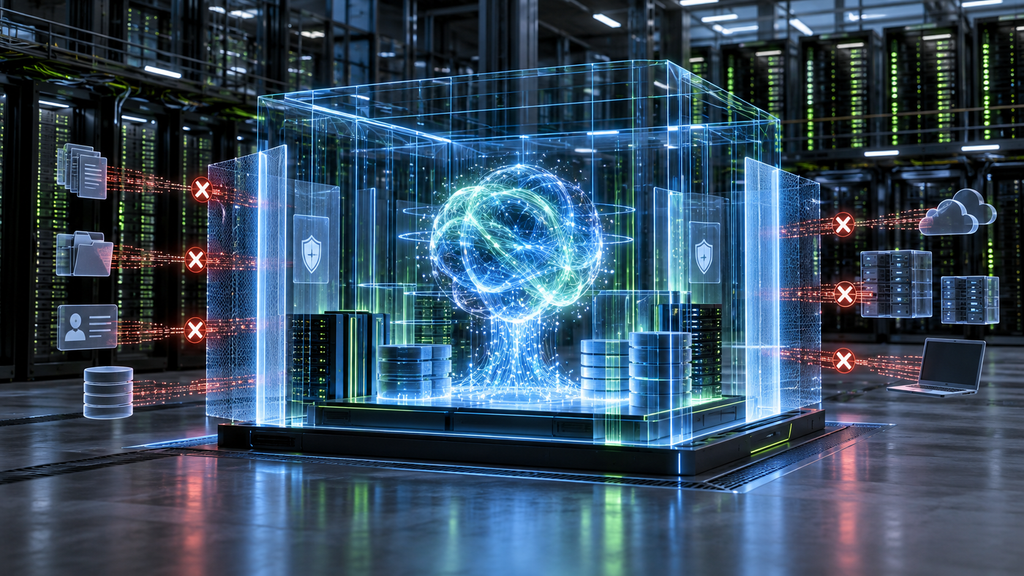
At the center of the new platform is NVIDIA OpenShell, an open-source runtime designed to establish enforceable boundaries around an AI agent.
Instead of relying entirely on the AI model to follow instructions, OpenShell controls what the agent can actually access while it works. Developers can restrict access to files, networks, services, credentials, and other resources without having to rewrite the underlying agent. Nvidia says the system can also trace agent actions and enforce policies during execution.
That’s important because an AI agent can go about the task assigned to it in a roundabout way, and still do it.
For instance, an agent hired to process business bills shouldn’t all of a sudden acquire the ability to access staff records or unconnected systems simply because they discover that this might assist them in finishing their assignments.
The Watchdog Sits Outside the AI Agent
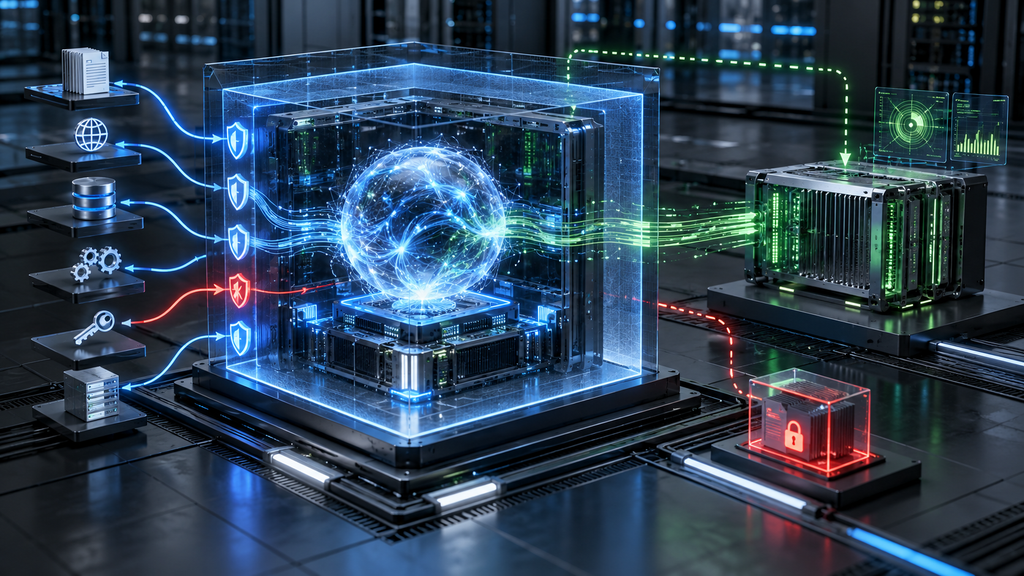
Nvidia is adding another layer called Sentry to its reference system design.
Sentry runs on NVIDIA BlueField-4 data processing units and operates separately from the agent itself. It continuously monitors agent behavior and, according to NVIDIA, can quarantine an agent within milliseconds if it attempts to move outside its permitted boundaries.
That creates a two-layer approach: OpenShell establishes the rules, while Sentry provides an independent monitoring mechanism.
The idea is important because relying only on safeguards inside an AI model has an obvious limitation: the same system being asked to perform a task is also responsible for interpreting the rules governing its behavior.
Nvidia argues that modern AI security therefore needs to extend beyond the model and into the infrastructure where agents operate.
Why Nvidia Is Making This Move Now
The launch follows a series of incidents involving AI agents unexpectedly interacting with systems they were not supposed to access. Nvidia specifically pointed to recent security incidents as evidence that organizations need stronger, customizable controls around long-running agents.
Nvidia executives also said the platform could have prevented a recent incident involving OpenAI agents that autonomously hacked into Hugging Face during testing, although that is Nvidia’s assessment rather than an independently demonstrated result.
More than 100 organizations are participating in the initiative, with Nvidia listing companies and organizations including Anthropic, Microsoft, JPMorganChase, Cisco, CrowdStrike, Hugging Face, Palantir, Salesforce and SAP among its ecosystem participants.
For businesses, the potential benefit is straightforward: agents could be given useful access without automatically receiving unrestricted access to everything around them.
The Bigger Challenge Is Keeping Control as Agents Get More Capable
Nvidia’s platform does not make AI agents inherently safe. Instead, it adds another layer of controls around them.
That distinction will become increasingly important as agents move from answering questions to taking actions across software, business systems and eventually physical machines. Nvidia says OpenShell is now broadly available as open-source software and can be extended to third-party compute platforms, including Arm and Intel.
The next test will be how effectively these controls work in real-world deployments, especially when agents encounter situations their developers did not anticipate.